Crypto Trading Bot Failure Modes: 15 Critical Risks & Tests (2026)
Crypto trading bot failure modes are the specific ways an automated strategy can produce an unsafe, incorrect, or unavailable outcome. This guide maps 15 failures from biased research to orphan orders, scores them with an interactive FMEA model, and turns each risk into a control, test, and recovery decision before real capital is exposed.
Last fact-checked: September 22, 2026 · Educational content for U.S. readers · No profit, availability, or loss-limit guarantee
Coinrule offers rules-based automation and a demo exchange workflow. Use simulation to validate conditions, notifications, and stop logic—not to infer that live execution will match a demo.
A Practical Crypto Trading Bot Failure Modes Framework
A failure mode describes how a system can fail. Its cause is the condition that triggers it; its symptom is what an operator first observes; its effect is the operational or financial consequence. A control prevents, detects, contains, or recovers from the failure. Evidence proves that the control actually worked. Keeping these terms separate stops a vague symptom such as “orders look wrong” from becoming the entire diagnosis.
This page treats crypto trading bot failure modes as an engineering and operating problem. The companion crypto trading bot monitoring guide explains which live signals to watch. The risk management framework covers exposure limits and kill switches, while the API security guide covers credentials and permissions. Here, the unit of analysis is a broken path and the test that demonstrates it is controlled.
A credible crypto trading bot failure modes register is specific to one strategy, venue, account type, deployment, and operating team. A grid bot on spot markets and a leveraged derivatives system do not share identical effects. Record assumptions, owners, last test dates, and residual risk rather than copying generic scores.
Crypto Trading Bot Failure Modes FMEA Calculator
Score one failure at a time from 1 to 5. Severity measures the worst credible effect. Occurrence estimates how often the failure might arise under the defined operating conditions. Detectability is reversed: 1 means detection is almost certain and prompt; 5 means the failure is difficult to detect before harm. The risk priority number, or RPN, is severity × occurrence × detectability.
Illustrative bands: 1–20 lower, 21–50 moderate, 51–80 high, 81–125 critical. Any severity-5 item, account-state mismatch, orphan order, suspected credential breach, or uncontrolled exposure overrides the numeric band and requires incident treatment. Do not use RPN to average away a catastrophic effect.
Manual method: multiply severity × occurrence × detectability. Apply the critical override whenever severity is 5 or exposure, account state, or credentials are uncertain.
For every entry, write the current score and a target residual score after controls. A lower residual score is credible only when the control has an owner, a test procedure, a pass condition, and dated evidence. If detectability improves because an alert exists, test the full route through delivery and acknowledgement—not merely the internal rule.
15 Crypto Trading Bot Failure Modes at a Glance
This crypto trading bot failure modes matrix is a triage map. It does not assign universal scores because severity changes with leverage, order size, liquidity, permissions, and the strategy’s holding period. Start with the worst credible effect in your own environment.
| # | Failure mode | Early symptom | Primary effect | Minimum proof test |
|---|---|---|---|---|
| 1 | Lookahead bias | Implausibly smooth backtest | Nonexistent edge reaches production | Bias analyzer plus causal feature review |
| 2 | Overfitting or selection bias | Performance collapses out of sample | Rules memorize history | Untouched holdout and walk-forward test |
| 3 | Regime change or edge decay | Live distribution drifts | Valid historical behavior stops working | Shadow comparison and retirement trigger |
| 4 | Stale, gapped, or corrupt data | Old timestamps or sequence gaps | Decisions use false market state | Freeze feed and inject a sequence gap |
| 5 | Wrong configuration or units | Unexpected size, side, market, or leverage | Incorrect exposure | Schema validation and deployment diff |
| 6 | Runaway loop or duplicate process | Order rate or instance count doubles | Repeated orders | Start a competing instance; verify lock |
| 7 | Unknown order status | Timeout after submission | Blind retry duplicates an order | Drop acknowledgement; query by client ID |
| 8 | Retry storm and rate-limit cascade | Rising 429/5xx and queue depth | Self-amplified outage | Throttle API; verify bounded backoff |
| 9 | Exchange-filter rejection | Precision or notional error | Protection or entry never reaches venue | Boundary-value order validation |
| 10 | Partial-fill or cancel race | Local quantity differs from fills | Orphan exposure | Fill during cancel; reconcile final state |
| 11 | Liquidity, slippage, or gap | Fill cost exceeds assumption | Expected edge disappears | Size ladder and adverse-book simulation |
| 12 | Authentication or permission failure | Invalid signature, timestamp, or key | Bot loses control or key is abused | Rotate/revoke key and test least privilege |
| 13 | Position or ledger mismatch | Exchange and bot disagree | Unknown actual exposure | Manual trade/fee injection and reconciliation |
| 14 | Infrastructure or dependency failure | Crash loop, disk full, database unavailable | State loss or unavailable controls | Kill process and dependency; verify persistence |
| 15 | Monitoring or recovery failure | No alert, unsafe auto-restart | Failure persists or repeats silently | Break alert route and rehearse restart gate |
The 15 Critical Crypto Trading Bot Failure Modes
The sections below use one repeatable structure: symptom, mechanism, control, and proof test. That format makes crypto trading bot failure modes operational. “Be careful” is not a control; a deterministic guard with a recorded test result can be.
Mode 1Crypto Trading Bot Failure Modes: Lookahead Bias
Symptom: the backtest looks unusually smooth, entries align almost perfectly with later price moves, or performance collapses when the same rules run candle by candle. Mechanism: a feature, normalization, merge, or indicator calculation accidentally uses data that would not have existed at decision time. A negative shift, whole-period mean, or improperly aligned higher-timeframe series can leak the future into the past.
Control: define the information set available at every timestamp, calculate features causally, and compare batch results with an incremental replay. Freqtrade’s official lookahead-analysis documentation explains how biased signals can make a backtest appear profitable. Test: run an automated bias analyzer, inspect every feature with future-access potential, and reproduce a sample of decisions using only prior observations. Block deployment if signal timing changes. Among crypto trading bot failure modes, this one is deceptive because valid software can execute invalid research.
Mode 2Crypto Trading Bot Failure Modes: Overfitting and Selection Bias
Symptom: the chosen parameter set dominates in the optimization period but deteriorates on unseen dates, nearby settings behave very differently, or repeated searches keep producing a new “best” result. Mechanism: enough rules, assets, date ranges, and parameter trials can fit noise. Selecting the winner after viewing many results also makes its reported performance optimistic.
Control: reserve a genuinely untouched holdout, limit the search space before testing, evaluate stability across neighboring parameters, and include fees, spread, latency, and realistic fills. Use walk-forward analysis without reusing the final holdout for redesign. Test: freeze the rules and evaluate them once on unseen data and then in crypto bot paper trading. Approval requires acceptable behavior across regimes, not merely one high headline return. Of all crypto trading bot failure modes, overfitting is the reason one winning backtest proves so little.
Mode 3Crypto Trading Bot Failure Modes: Regime Change and Edge Decay
Symptom: trade frequency, holding time, hit rate, slippage, drawdown, or feature distributions drift beyond the tested range even though the code is unchanged. Mechanism: market structure, volatility, liquidity, participants, correlations, fees, or venue rules change. A strategy can be implemented correctly and still lose relevance.
Control: define the population and regime assumptions behind each rule, monitor live-versus-research distributions, cap exposure during uncertainty, and predefine degradation and retirement triggers. Test: replay stressful historical windows, run the candidate in shadow mode beside production, and verify that a breached retirement trigger blocks new entries. Do not silently re-optimize until the system “works”; that restarts the selection-bias problem. Crypto trading bot failure modes also include valid logic whose economic assumptions have expired.
Mode 4Crypto Trading Bot Failure Modes: Stale or Corrupt Data
Symptom: event timestamps stop advancing, sequence numbers jump, prices repeat despite active markets, candles arrive out of order, or a second source materially disagrees. Mechanism: a websocket can remain connected while a subscription is stale; reconnect logic can miss the required snapshot; local clocks and time zones can misalign bars; corrupted data can pass through valid numeric fields.
Control: validate event time, receive time, sequence continuity, schema, range, and source identity. Require an exchange-documented resynchronization path and block decisions until the feed is complete. Test: pause messages, duplicate an update, inject an out-of-order sequence, and corrupt one value in a non-live environment. The expected result is a fail-closed trading state, a specific alert, and a clean rebuild before processing resumes. Within crypto trading bot failure modes, bad input can invalidate every downstream decision at once.
Mode 5Crypto Trading Bot Failure Modes: Wrong Configuration or Units
Symptom: the bot trades the wrong symbol, reverses a side, sizes in quote currency instead of base units, connects to production instead of sandbox, or uses an unexpected margin mode. Mechanism: permissive configuration, environment-variable drift, copy-pasted defaults, implicit units, or a venue adapter that interprets contract quantity differently can change exposure without changing strategy code.
Control: use a typed schema, explicit units, an environment banner, bounded values, immutable versioned configuration, and a human-readable deployment diff. Reject unknown keys rather than ignoring them. Test: deliberately provide an invalid market, excessive size, missing risk limit, and production credential in a test deployment. Each must fail before order submission. Record the approved configuration hash with every decision so forensic review can reproduce behavior. Crypto trading bot failure modes caused by configuration often bypass otherwise correct strategy code.
Mode 6Crypto Trading Bot Failure Modes: Runaway or Duplicate Process
Symptom: signal evaluations, order attempts, or notification volume suddenly multiply; two hosts report the same bot identity; or restarts overlap with a still-running instance. Mechanism: an unbounded loop can reprocess one event, a queue can redeliver work, or an orchestrator can start a replacement before the original loses leadership.
Control: enforce a single-writer lease, unique deployment identity, idempotency keys, maximum order frequency, bounded queues, and account-level exposure guards independent of the strategy loop. Test: launch a competing instance and replay the same signal twice. Only one process should acquire authority, and duplicate work should produce the same result without a second order. A rate alarm is useful, but prevention must happen before the exchange sees repeated submissions. Crypto trading bot failure modes involving duplication demand prevention at both process and order levels.
Mode 7Crypto Trading Bot Failure Modes: Unknown Order Status
Symptom: an order request times out or returns a server error after submission, but no definitive accepted or rejected state is available locally. Mechanism: the venue can accept an order while the response is lost. Binance’s official Spot REST API guidance states that a timeout can leave execution status unknown and directs clients to confirm through the user data stream or an order query.
Control: assign a unique client order ID before sending, persist intent first, represent STATUS_UNKNOWN explicitly, and query venue state before any retry. Test: drop the acknowledgement after the simulated venue accepts the order. The bot must find the original by client ID, reconcile fills, and avoid a duplicate. This is one of the highest-priority crypto trading bot failure modes because a naive retry can add exposure. Crypto trading bot failure modes with ambiguous side effects require reconciliation before repetition.
Mode 8Crypto Trading Bot Failure Modes: Retry Storm and Rate Limits
Symptom: timeout, error, and rate-limit counts rise together; request queues grow; retries synchronize across workers; or a partial venue problem becomes total API loss. Mechanism: immediate unlimited retries increase load on the same dependency that is already failing. Google SRE’s cascading-failure guidance warns that retries can amplify overload.
Control: use bounded exponential backoff with jitter, a retry budget, endpoint-aware rate accounting, circuit breakers, concurrency limits, and a queue expiration rule. Reuse the exchange client where the library’s limiter is attached; CCXT’s official manual documents built-in rate limiting and warns against repeatedly recreating exchange instances. Test: throttle the adapter and confirm request volume falls, stale work expires, and essential reconciliation keeps priority. Some crypto trading bot failure modes worsen because the recovery traffic becomes the outage.
Mode 9Crypto Trading Bot Failure Modes: Exchange-Filter Rejection
Symptom: the venue rejects an order for tick size, step size, precision, balance, price band, or minimum notional; a protective exit may never become active. Mechanism: exchange filters can vary by symbol and change over time. Floating-point rounding, stale metadata, fees, and locked balances make a locally “valid” quantity invalid at submission.
Control: load venue metadata, validate price and quantity with decimal arithmetic, round in the permitted direction, reserve fees, refresh filters, and distinguish a rejected entry from a rejected protective action. Binance documents symbol and exchange filters in its official filter reference. Test: exercise values immediately below, at, and above each boundary. Confirm the bot blocks invalid orders locally and escalates any rejected risk-reduction order. Among crypto trading bot failure modes, filter rejection is especially urgent when it blocks risk reduction.
Mode 10Crypto Trading Bot Failure Modes: Partial-Fill and Cancel Race
Symptom: the bot believes an order was canceled while the venue reports an additional fill; remaining quantity is wrong; or replacement plus late fill exceeds the intended position. Mechanism: fills and cancellation messages race across asynchronous channels. A cancel request is not a terminal state, and cumulative fills may update while the request is in flight.
Control: model partial fills explicitly, process events idempotently, calculate remaining quantity from exchange-confirmed cumulative fills, and wait for a terminal venue state before replacing. Reconcile the final position after each cancel/replace cycle. Test: inject a partial fill, issue a cancel, then deliver another fill before the cancellation confirmation. The replacement must use the final remaining quantity or be blocked. The ledger must equal exchange state before new exposure is allowed. Crypto trading bot failure modes involving races require event-order tests, not only happy-path unit tests.
Mode 11Crypto Trading Bot Failure Modes: Liquidity, Slippage, and Gaps
Symptom: average fill price departs from the decision benchmark, market impact rises with size, spread widens, or a stop executes far beyond its trigger. Mechanism: backtests often assume sufficient depth at one price. Live orders consume multiple book levels, compete for queue priority, face latency, and encounter gaps. Stop orders trigger execution logic; they do not guarantee a particular fill.
Control: model depth and fees conservatively, cap participation and order size, monitor live slippage by regime, choose order types deliberately, and define maximum acceptable execution cost. Test: replay adverse order books, apply size ladders, widen spread and latency assumptions, and verify that the bot reduces size or refuses entry when the expected edge no longer covers cost. The CFTC’s virtual-currency advisory underscores volatility and leverage risks. These crypto trading bot failure modes can occur even when every order is technically valid.
Mode 12Crypto Trading Bot Failure Modes: Authentication and Permissions
Symptom: invalid-signature or timestamp errors appear, authenticated streams stop, permissions are insufficient, a rotated key remains cached, or an unexpectedly broad key is used. Mechanism: clock drift changes signed-request validity; key rotation can be incomplete; IP allowlists and permissions can change; a leaked key can give an attacker capabilities the bot never needed.
Control: synchronize time, isolate secrets, use trading-only least privilege, disable withdrawals, restrict source IP where supported, separate environments and bots, rotate credentials through a rehearsed process, and alert on permission changes. Test: revoke and rotate a sandbox key, skew the test clock, remove one permission, and verify fail-closed behavior without logging secrets. Suspected credential compromise is a critical override in any crypto trading bot failure modes register. Security-related crypto trading bot failure modes require containment beyond restarting the application.
Mode 13Crypto Trading Bot Failure Modes: Position or Ledger Mismatch
Symptom: internal position, available balance, fees, open orders, or realized quantity does not match the exchange. Mechanism: a missed fill, manual trade, transfer, fee asset, funding event, another bot, rounding error, or database rollback can split local truth from venue truth.
Control: treat exchange-confirmed orders, fills, positions, and balances as the reconciliation source; retain an immutable event trail; assign ownership to each account; and freeze affected new entries on unexplained differences. Test: make a permitted manual change in a sandbox, omit one simulated account event, and apply a fee in a different asset. The bot must detect the mismatch, preserve exits where safe, and require explicit reconciliation—not overwrite evidence to make the numbers agree. Of all crypto trading bot failure modes, uncertain account state should never be cleared by assumption.
Mode 14Crypto Trading Bot Failure Modes: Infrastructure Failure
Symptom: the worker freezes or restarts, disk fills, database writes fail, DNS cannot resolve, the exchange adapter changes behavior, or the host disappears. Mechanism: trading logic depends on an operating system, network, storage, clock, libraries, and external services. A process restart can also lose unpersisted intent and repeat work.
Control: persist intent and order state before side effects, make consumers idempotent, monitor capacity, pin and test dependencies, back up critical state, and define degraded behavior. Container restart policies improve availability but are not proof of correctness; Docker’s official restart-policy documentation explains their operating conditions. Test: kill the process at each order stage, exhaust test storage, and interrupt the database. Recovery must reconcile before new submissions.
Mode 15Crypto Trading Bot Failure Modes: Monitoring and Recovery Failure
Symptom: a failure persists without a page, an alert reaches a muted channel, the on-call response has no owner, or an automatic restart returns the bot to trading before state is reconciled. Mechanism: teams often test the trading path but not the safety path. Monitoring can share the same failed dependency, and a restart can erase transient evidence while the original exchange-side effect remains.
Control: use independent synthetic checks, scheduled notification tests, secondary critical routing, immutable logs, a written incident runbook, and a restart gate that verifies data, orders, positions, balances, credentials, configuration, and alert delivery. Test: break the primary notification channel, stop the heartbeat, and restart with an unresolved order. The system must alert through the backup route and keep new entries disabled until a human or approved workflow clears every gate.
How to Test Crypto Trading Bot Failure Modes Safely
Failure injection proves whether controls behave under adverse conditions. Run crypto trading bot failure modes tests in a local harness, replay environment, paper account, sandbox, or exchange testnet whenever possible. A test that could create unintended orders, burden a venue, affect other market participants, or expose credentials does not belong in a live market. If a limited live verification is unavoidable, preapprove the scope, smallest safe size, stop condition, owner, and rollback.
| Safe test | Injected condition | Required result | Evidence to retain |
|---|---|---|---|
| Stale feed | Pause or age market events | New decisions stop; stale-data alert fires | Event timestamps, blocked-decision reason, alert receipt |
| Unknown order status | Drop the submission response after acceptance | Query by client ID; no blind retry | Intent record, venue query, single exchange order |
| Duplicate intent | Replay the same client ID or message | Idempotent result; no second order | Deduplication log and order count |
| Rate limiting | Return throttling responses | Backoff with jitter; retry budget remains bounded | Request-rate graph, queue age, breaker state |
| Partial fill | Fill only part of the requested quantity | Remaining amount and position reconcile | All fill IDs, cumulative quantity, final ledger |
| Cancel/fill race | Deliver a fill during cancellation | Terminal state queried before replacement | Ordered event trace and final exposure |
| Invalid filter | Use a boundary-breaking size or price | Local validation blocks submission | Filter version and rejection reason |
| Process crash | Terminate at each order-lifecycle stage | Restart reconciles before new entries | Persisted state, restart log, reconciliation report |
| External account change | Simulate a manual trade or fee adjustment | Mismatch alert; affected entries freeze | Before/after account snapshots and acknowledgement |
| Alert-channel failure | Disable the primary notification path | Backup route receives critical alert | Delivery and acknowledgement timestamps |
- Define one hypothesis. State the injected fault, expected system state, forbidden behavior, time limit, and pass condition.
- Isolate the environment. Verify account, API endpoint, permissions, symbols, balances, and any outbound connector before starting.
- Capture a baseline. Save configuration hash, version, open orders, positions, balances, clocks, and healthy telemetry.
- Inject one fault. Keep the test observable and reversible; do not combine failures until each single path passes.
- Verify containment and recovery. Confirm the unsafe action stopped, evidence survived, state reconciled, and restart gates remained closed until proof existed.
- Record residual risk. Update the crypto trading bot failure modes register, owner, FMEA score, last test date, result, and next review trigger.
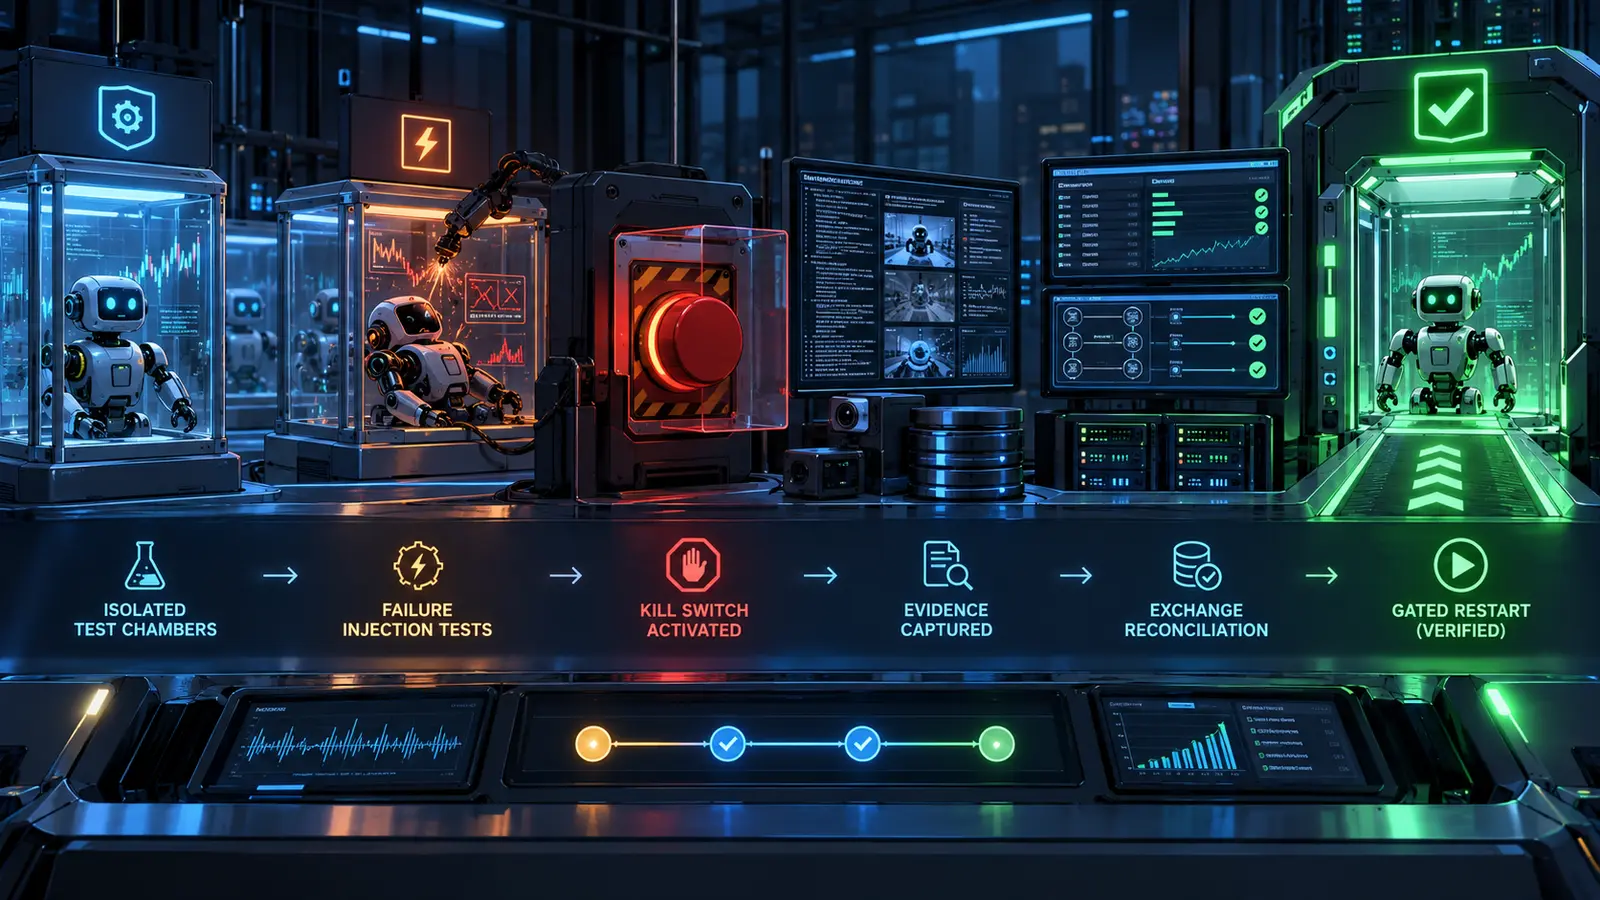
Control Hierarchy for Crypto Trading Bot Failure Modes
Use several independent layers because no single control covers every failure. The strongest design removes the unsafe path; the weakest merely reports harm after it occurs. Apply the hierarchy to every high-priority entry in the crypto trading bot failure modes register.
| Layer | Purpose | Trading-bot example | Proof |
|---|---|---|---|
| Eliminate | Remove an unnecessary hazard | Withdrawal permission is absent from the trading key | Permission inspection and denied withdrawal test |
| Guard | Block invalid action before side effect | Schema, symbol filter, size cap, single-writer lease | Boundary and duplicate-instance tests |
| Detect | Identify an unsafe or degraded state | Stale-feed, unknown-order, and position-mismatch alert | End-to-end alert receipt and acknowledgement |
| Contain | Limit blast radius | Freeze new entries for one bot or symbol while exits remain governed | Scoped fault-injection result |
| Recover | Restore a known-correct state | Venue reconciliation, controlled restart, rollback | Orders, fills, balances, and positions all match |
| Evidence | Make behavior reconstructable | Immutable events, versions, configuration hashes, test reports | Independent incident timeline reconstruction |
Separate a kill switch from process termination. Stopping a worker can also stop protective management while orders remain live at the venue. A safe response must define what happens to open orders, positions, pending withdrawals or transfers if applicable, and each external control. For grid-specific controls, use the when to stop a grid bot decision framework. For backtest realism, see the crypto grid bot backtesting guide.
Who Owns Crypto Trading Bot Failure Modes?
Failure ownership changes with the deployment model, but responsibility never disappears. A managed service can reduce server maintenance while adding platform dependency and configuration risk. Self-hosting adds control but also makes the operator responsible for availability, secrets, updates, telemetry, and recovery.
| Setup | Operator typically owns | Provider or venue typically owns | Main tradeoff |
|---|---|---|---|
| Managed automation platform | Rule logic, key permissions, account limits, notification review, platform selection | Application hosting and platform execution service | Lower infrastructure burden; greater vendor dependency |
| Self-hosted bot | Code, host, database, network, secrets, monitoring, upgrades, incident response | Exchange endpoints and matching engine | Maximum control; maximum operating workload |
| Exchange-native bot | Parameters, funds, market choice, supervision, account security | Bot implementation and exchange infrastructure | Fewer integrations; concentration on one venue |
| Signal or copy workflow | Provider diligence, sizing, delay, divergence, stop policy, account reconciliation | Signal publication or copy mechanism | Simple setup; reduced transparency and timing control |
Cryptohopper includes paper trading and configurable automation features. Evaluate exchange support, rule behavior, key scope, failure notifications, and recovery controls for your own account before live use.
A vendor status page does not replace account-level evidence. Regardless of setup, keep a current inventory of bots, venues, API keys, owners, strategies, maximum approved exposure, notification routes, and emergency procedures. Ask which crypto trading bot failure modes the product prevents, which it only detects, which remain yours, and whether you can export enough history to reconstruct an incident.
Bitsgap offers grid and other automated strategies. Check supported venues, range behavior, order handling, fees, API permissions, and what happens when price leaves the configured grid.
Before choosing a platform, compare our Bitsgap vs Cryptohopper analysis, Bitsgap review, and Cryptohopper review. The broader best crypto trading bots guide covers selection criteria; the grid bot comparison narrows the field for grid strategies.
Costs, Risks, and Limitations
Managing crypto trading bot failure modes adds real cost. Self-hosted teams pay for engineering, compute, resilient storage, logs, metrics, paging, test environments, backups, security review, venue adapters, and incident response. Managed platforms convert part of that burden into subscription cost and vendor dependence. Both models consume operator time.
An FMEA score is subjective and ordinal. Multiplication creates a convenient rank, not a statistically calibrated loss estimate. Two different combinations can produce the same RPN while having very different consequences. Review severity separately, retain critical overrides, and do not claim that a test proves all future conditions. Testnets may use different liquidity, filters, latency, and failure behavior from production.
Trading records also have accounting and tax implications. Preserve orders, fills, fees, transfers, and configuration history in exportable form, but obtain qualified advice for your jurisdiction. This guide addresses operational design, not tax, legal, cybersecurity, or investment advice.
Who This Crypto Trading Bot Failure Modes Framework Is For
| Best fit | Why it helps | Not a fit | Why not |
|---|---|---|---|
| Bot builders and technical operators | Turns architecture risks into testable controls and release gates | Anyone seeking guaranteed profit | Reliability controls cannot create a trading edge or remove market risk |
| Serious users of managed bot platforms | Clarifies what the platform owns and what the account owner must verify | Set-and-forget users | Keys, venues, rules, and market conditions continue to change |
| Teams preparing a live launch | Provides a pre-live test suite and incident vocabulary | Users unable to reconcile exchange state | Unknown orders or positions cannot be managed safely |
| Operators reviewing an incident | Supports root-cause, control, evidence, and residual-risk updates | Users relying only on backtest return | Backtests do not prove live execution or recovery behavior |
Pros
- Creates one consistent language for research, execution, infrastructure, and operating failures.
- Prioritizes crypto trading bot failure modes without pretending all risks are equal.
- Connects each risk to a specific control, owner, test, and deployment gate.
- Improves incident evidence and makes repeated failures easier to identify.
Cons
- Scores contain judgment and can create false precision if the rationale is not recorded.
- Test environments cannot reproduce every venue, liquidity, or production dependency.
- Documentation becomes stale unless change events trigger reassessment.
- More controls add implementation and maintenance complexity that can itself fail.
Crypto Trading Bot Failure Modes Pre-Live Checklist
- □ Name the strategy, venue, account type, environment, version, owner, and maximum approved exposure.
- □ Build a crypto trading bot failure modes register with cause, symptom, effect, severity, occurrence, detectability, controls, and residual risk.
- □ Prove research inputs are causal and retain an untouched holdout plus realistic cost assumptions.
- □ Validate configuration schema, units, symbols, precision, notional, market type, leverage, and environment.
- □ Enforce single-writer authority, idempotent processing, unique client order IDs, and bounded order frequency.
- □ Represent unknown order status and partial fills explicitly; never infer rejection from a timeout.
- □ Reconcile orders, fills, fees, balances, and positions against exchange-confirmed state.
- □ Use least-privilege API keys, no withdrawal capability, separate environments, and a rehearsed rotation path.
- □ Set retry budgets, exponential backoff with jitter, queue expiry, circuit breakers, and rate-limit telemetry.
- □ Test process, database, network, storage, dependency, feed, notification, and restart failures safely.
- □ Write containment rules that distinguish new entries, exits, cancellations, and account-wide emergency action.
- □ Require a restart gate: correct config, fresh data, healthy credentials, reconciled state, functioning alerts, and retained evidence.
- □ Schedule a review after incidents and material changes to code, venue, strategy, permissions, infrastructure, or capital.
For a grid system, add explicit checks for range exits, accumulated inventory, fees, capital allocation, and idle behavior. The grid bot not trading guide diagnoses inactivity, while the grid bot fees guide explains how turnover costs can erode an apparent edge.
Crypto Trading Bot Failure Modes FAQ
What are crypto trading bot failure modes?
Crypto trading bot failure modes are specific ways an automated trading system can produce an incorrect, unsafe, or unavailable result. Examples include biased research, stale data, duplicate orders, ambiguous order status, partial-fill races, position mismatches, credential failures, infrastructure outages, and unsafe restarts.
What is the most dangerous bot failure?
There is no universal single winner. Unknown or uncontrolled exposure, compromised credentials, duplicate orders, and exchange-versus-local state mismatches deserve critical treatment because delay can compound harm. Your account type, leverage, liquidity, permissions, and order size determine the worst credible effect.
Does a stopped bot mean the account is safe?
No. Open orders can remain at the venue, positions can keep moving, funding or fees may continue, and protective management may stop with the process. Verify orders, positions, balances, and venue-native protections before declaring a safe state.
How should a bot handle an order timeout?
Record the status as unknown, query the exchange using the client order ID or venue order data, inspect authenticated account events, and reconcile before retrying. A timeout does not prove the order was rejected.
What is a good RPN threshold?
No universal threshold is valid. The calculator’s bands are illustrative. Document why each rating applies, handle severity separately, use critical overrides for uncontrolled exposure or uncertain account state, and compare scores within the same defined system.
How often should failure tests run?
Run them before first live use and after material changes to code, configuration, venue, account, permissions, dependencies, or infrastructure. Repeat critical recovery and alert-path tests on a documented schedule based on risk and change frequency.
Can paper trading reveal every failure?
No. Paper trading is useful for logic, state transitions, notifications, and operator practice, but it may not reproduce production liquidity, queue position, partial fills, rate limits, outages, or venue-specific edge cases. Combine it with mocks, replay, testnet, and tightly controlled verification.
Can crypto trading bot failure modes be eliminated?
Some hazards can be removed, while others can only be reduced, detected, contained, or recovered from. Markets, exchanges, software, networks, and operators remain uncertain. The goal is controlled residual risk with explicit evidence—not a claim of failure-proof trading.
Final Verdict: Design the Bot Around Failure
The strongest crypto trading bot failure modes program begins before deployment. It rejects noncausal research, validates data and configuration, makes every order idempotent and traceable, reconciles with exchange truth, limits retries, separates containment from shutdown, and rehearses recovery. A bot is not ready because its happy path works; it is ready for limited deployment only when its most credible failures produce bounded, observable, and recoverable outcomes.
Start with the 15-mode matrix, score the environment honestly, and select the top risks by severity and detectability. Run one safe injection at a time, store the evidence, lower residual scores only after controls pass, and require a new review when the system changes. Use crypto trading bot failure modes as a living operating register—not a one-time launch document.
Primary sources and further reading
- Binance Spot API — General API Information: timeout and unknown execution-status behavior.
- Binance Spot API — Filters: symbol, price, quantity, and notional rules.
- CCXT Manual: rate limiting, nonce behavior, errors, and exchange-instance guidance.
- Freqtrade — Lookahead Analysis: detecting future-data leakage in backtests.
- Google SRE — Addressing Cascading Failures: overload, retry amplification, and graceful degradation.
- Docker — Start Containers Automatically: restart-policy behavior and limits.
- CFTC — Virtual Currency Trading Advisory: volatility, leverage, and customer-protection considerations.